Essentials
£249/mo
or £199/mo billed annually
compliance, plus automation
Start free →Cloud Security Posture Management
Most cloud breaches don't start with a novel vulnerability. They start with something left open — a storage bucket without access controls, an IAM role with more permission than it needed, a security group facing the internet by accident. None of that shows up in a CVE database, because there's nothing to patch. There's only something to fix.
Connect an AWS, Azure, or GCP account read-only — you deploy a small CloudFormation stack that creates a role scoped to SecurityAudit and ViewOnlyAccess, gated by an ExternalId so only your account can be scanned, and revocable in one click. Misconfiguration scanning then runs against that account, checked line-by-line against CIS Benchmark controls. Findings land in the same prioritised queue as everything else in your Technology Posture Score, so a critical cloud misconfiguration competes for attention on the same terms as a critical CVE, instead of living in a separate tool nobody checks.
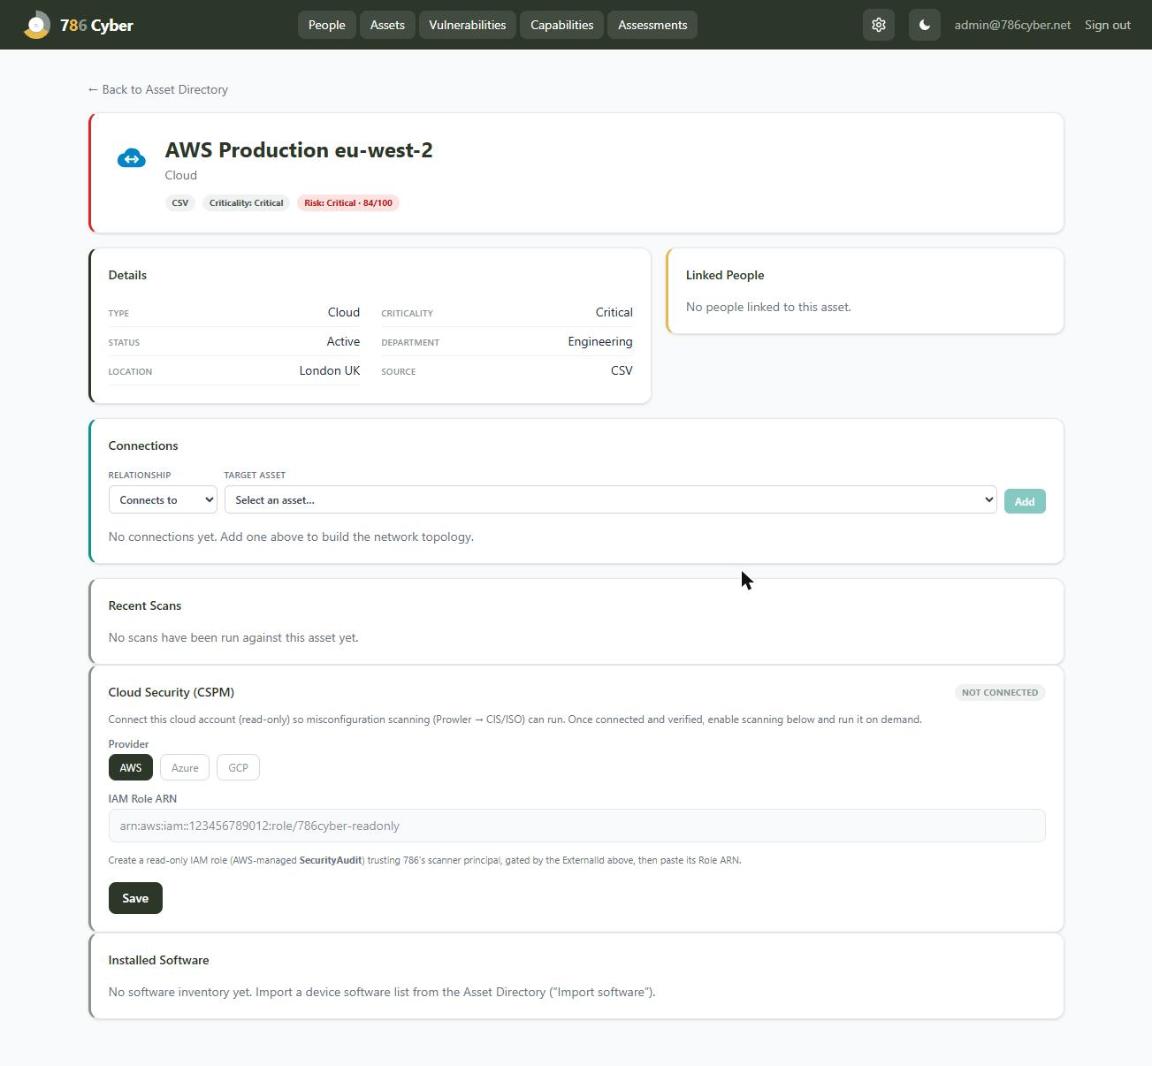
Under the hood this runs on Prowler — the open-source cloud security tool that checks live account configuration against CIS and ISO benchmarks — which is what CSPM (Cloud Security Posture Management) means in practice: not a one-time audit, but continuous, automated configuration checking.
Findings are scored and prioritised as misconfigurations and indicators of exposure — the things an attacker could actually use — so the queue reflects real risk rather than raw check counts.
Cloud Security Posture Management — automated, continuous checking of your cloud account configuration against a benchmark, rather than a one-time audit. It catches misconfigurations (open storage, over-permissioned roles, exposed security groups) that never appear in a CVE database because there is nothing to patch.
Read-only. You deploy a small CloudFormation stack that creates a role scoped to SecurityAudit and ViewOnlyAccess, gated by an ExternalId so only your account can be scanned — nothing that can change your environment, and revocable in one click.
Findings are checked line-by-line against CIS Benchmark controls, then scored and prioritised alongside the rest of your posture so the misconfigurations that expose you most surface first.
Pick a provider, deploy the read-only stack, done. 14-day free trial — no card required.
£249/mo
or £199/mo billed annually
compliance, plus automation
Start free →£549/mo
or £439/mo billed annually
for a scaling security function
Start free →£1,199/mo
or £959/mo billed annually
for an established programme
Start free →Just need to get compliant? Comply from £149/mo. Larger or regulated? Enterprise from £2,500/mo — talk to us →. All prices ex-VAT.