14 days free, no card Monthly from £149 Annual from £119/mo No lock-in. No surprises.

More than a platform.
A security philosophy built on standards.

Automated GRC and continuous compliance with smart policies and controls, backed by real security tooling, testing and validation.

Formalise your strategy. Choose from a growing universe of global security frameworks, or bring your own, and turn your processes and procedures into smart policies and controls.

Practise them every day. Connect your users, identities and privileges, your hardware and software, your cloud and your domains, and our security tooling tests what you actually run for threats, vulnerabilities and misconfigurations, on the schedule you set.

Build trust. Evidence is gathered once, counts everywhere it applies and is marked proven or declared. AI answers the security questionnaires, your auditor reviews it all in their own portal, and your Trust Centre shows customers where you stand.

Start free · No credit card required
ENVIRONMENT & PEOPLE TECHNOLOGY & THREATS POLICY & PROCESS Identify & Aggregate Protect & Validate Unify & Manage UNIFYING YOUR SECURITY ECOSYSTEM 786 Cyber One inventory. One control model.
  • Identify & Aggregate
  • Protect & Validate
  • Unify & Manage

Three pillars. Three motions, continuous across all of them. Hover to explore.

Works across
  • Windows
  • macOS
  • Linux
  • iOS
  • Android
  • Microsoft 365
  • Google Workspace
  • Cloud

Three pillars. One ecosystem.

Every capability maps to one of three disciplines — operating simultaneously, connected by a single risk picture.

Environment & People

Know who and what can reach your data — and how.

Identity is where most breaches start. 786 Cyber gives you a live view of every person in your organisation — their access, their MFA status, their risk score — and keeps it current as your team changes. Joiners, movers, leavers. Dormant accounts. Accounts switched off with no leaver on record. All surfaced before they become a problem.

Explore the pillar →

Technology & Threats

Know your exposure. Manage the risks that matter to your business.

You cannot protect what you cannot see. 786 Cyber builds your asset inventory, tracks your vulnerabilities, monitors your external exposure, and surfaces threats in plain English — not raw logs. Continuous, automated, and connected to your compliance posture.

Explore the pillar →

Policy & Process

Prove your standards are enforced every day, not just on audit day.

Compliance frameworks exist not because auditors require them, but because they encode what good security practice looks like. 786 Cyber maps your controls across 37 frameworks simultaneously — so closing one gap closes many. Your policies are generated, validated, versioned, and audit-ready.

Explore the pillar →

One platform, instead of a stack.

Twelve capabilities you would otherwise buy from twelve vendors, each holding its own version of the truth, built in and working as one. Already run one of them? Keep it: its output comes in as evidence.

See all twelve in detail ↓

The first fourteen days

What you'll see, and when.

Start free, no card. Every line below is something the trial shows you on that day — not something we say about ourselves.

Day 1

Connect

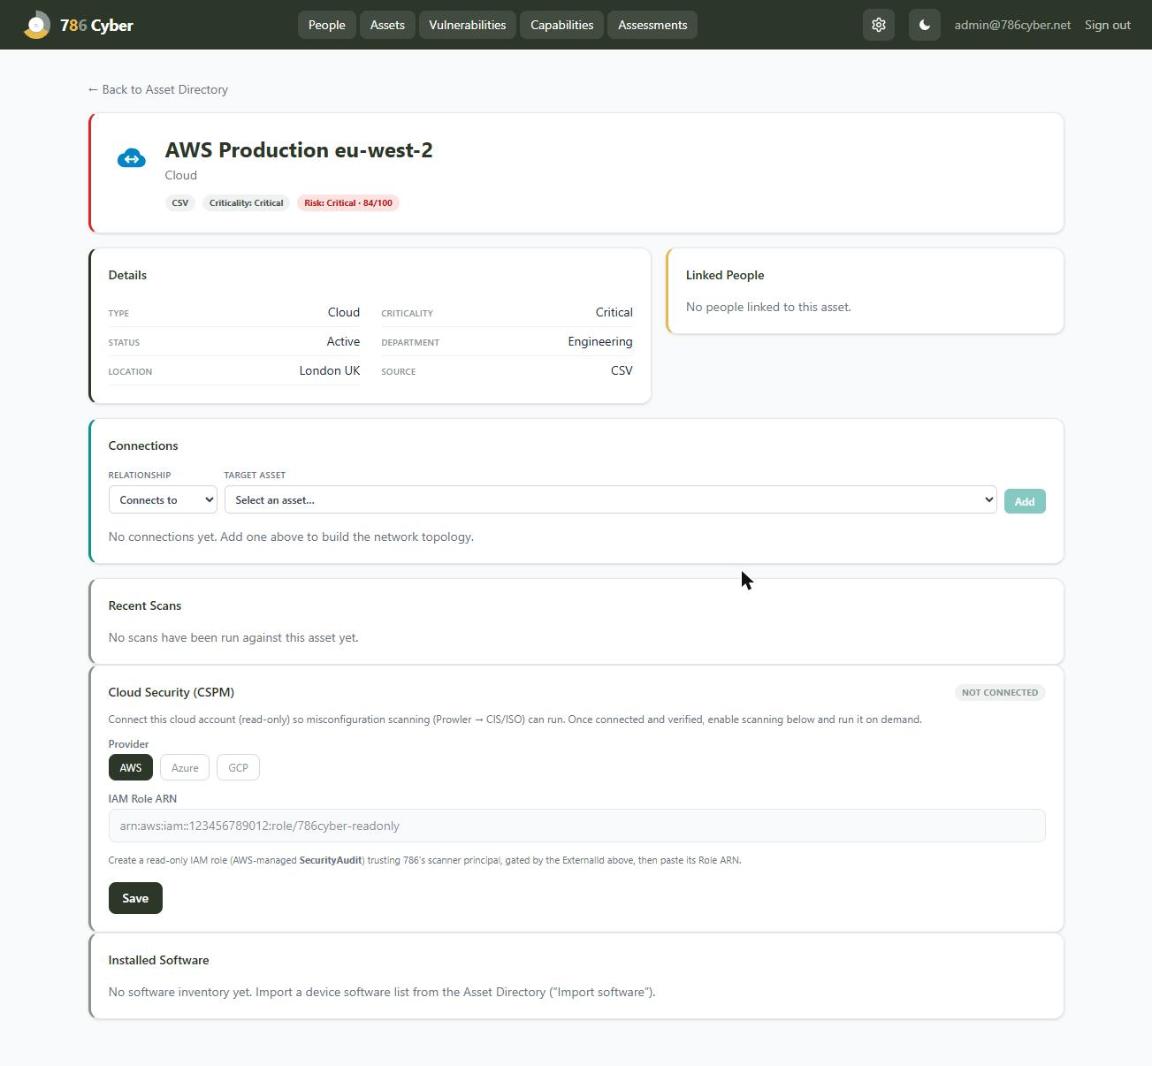
Microsoft 365 or Google Workspace, a domain and a cloud account — a read-only connection each, minutes not a project. By the end of the day you have every account with its MFA state, and the assets and subdomains you didn't know you had.

Connecting a cloud account — read-only, ExternalId-gated and revocable in one click.
Day 2

See

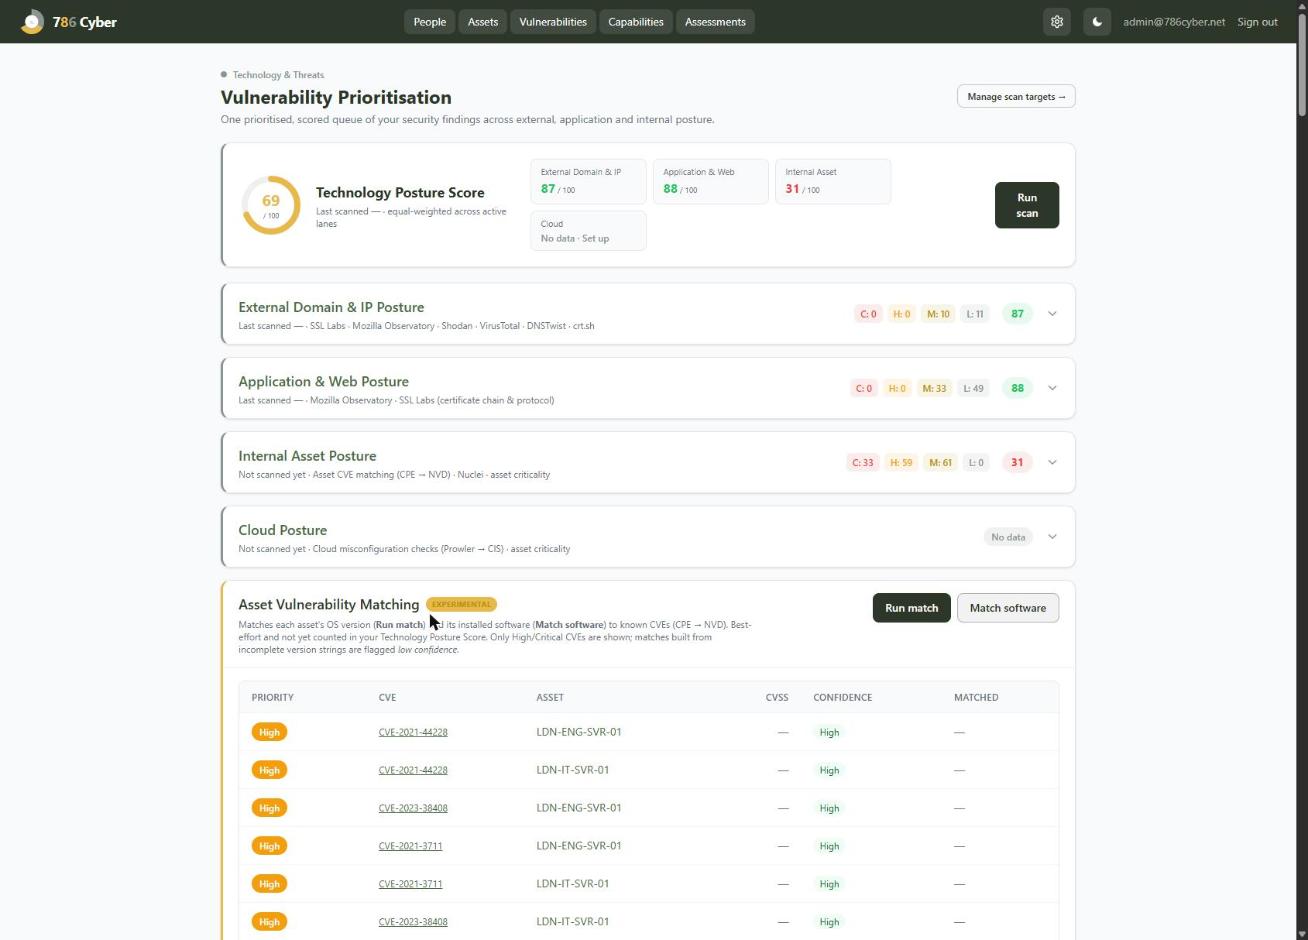
Exposed services, look-alike domains, credentials already in a breach, and your first prioritised queue — ranked by what attackers are exploiting, not by raw severity, each finding explained in plain English.

The dashboard — Technology Posture Score with all four posture lanes.
Day 7

Formalise

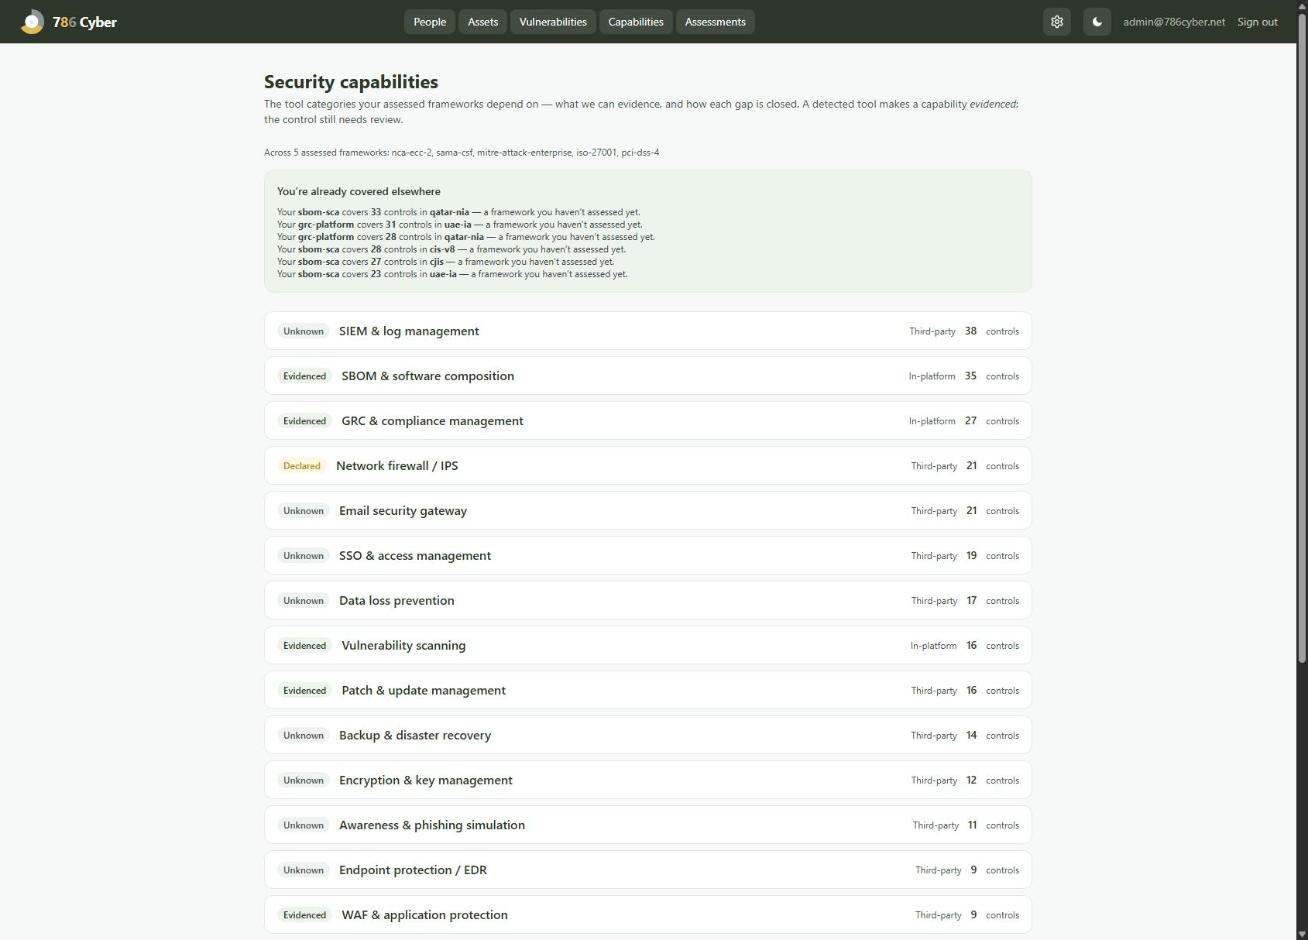
A gap report against your first framework, every control marked Evidenced, Declared or Unknown — and the evidence you already hold counted where it genuinely applies.

The capabilities page — each control marked Evidenced, Declared or Unknown.
Day 14

Stay

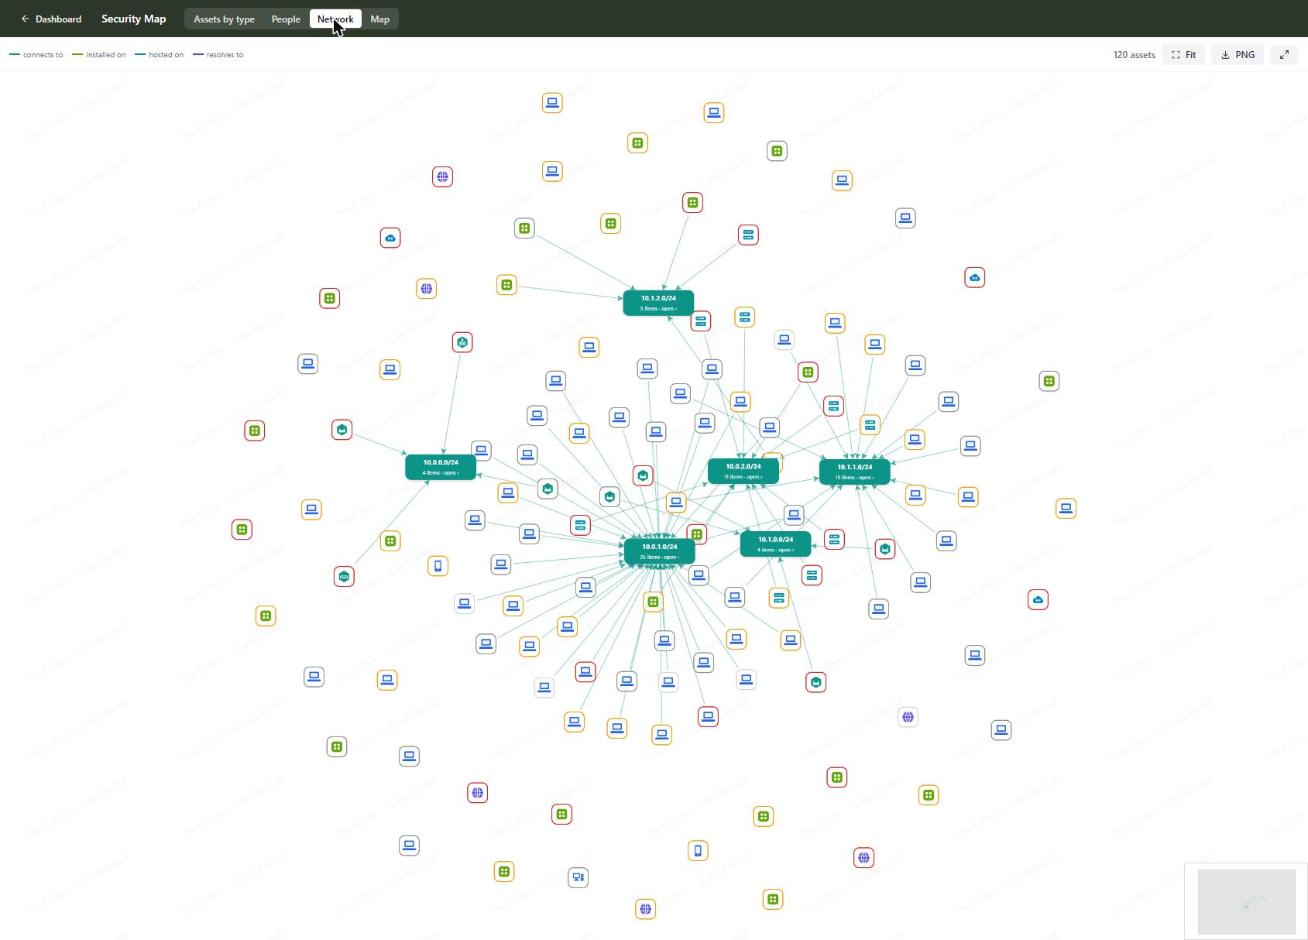
A new starter, a new device, a new vulnerability, a new exposure — you're told what changed and what to do. Pick a plan when you're ready; the mapping work you've done comes with you.

The network view — assets grouped into subnets with their connections.

Start free → No card. No sales call. No annual commitment on monthly plans.

Built on depth and maturity, for credibility and trust.

Every framework mapped against its authoritative source, every control cross-referenced, so your programme rests on something you can check.

37 Compliance frameworks, plus your own
2,976 Controls
2,300+ Control-level cross-mappings
9,700+ Assessment questions
25 years Industry experience behind every design decision
Explore the Security Universe →

Enhanced by AI. Grounded in your evidence.

AI does the paperwork. It drafts policies from your organisation's context, answers security questionnaires with every answer cited to your own policies and evidence, explains each finding in plain English, and checks your answers before an auditor does.

It never invents a figure and never marks a control met on its own. Every answer shows where it came from, and your team stays in charge.

The platform in detail

Three pillars. Twelve capabilities.

Everything below is built in. Some of it you may already run elsewhere, and that output comes in as evidence too.

See what's actually there.

Connect your directory, a domain and a cloud account. Fourteen days, no card, no sales call — and you will find something you didn't know you had.

Published pricing. Start free, decide later.

Essentials

£249/mo

or £199/mo billed annually

compliance, plus automation

Start free →

Business

£1,199/mo

or £959/mo billed annually

for an established programme

Start free →

Just need to get compliant? Comply from £149/mo. Larger or regulated? Enterprise from £2,500/mo — talk to us →. All prices ex-VAT.

We believe in empowering organisations with the capabilities to focus on what really matters — defining the right metrics, setting standards and controls, then monitoring execution. No fear. No lock-in. No complexity for its own sake.

Before chasing the latest threat narrative, make sure the basics are right. Most breaches happen through doors that were never locked.